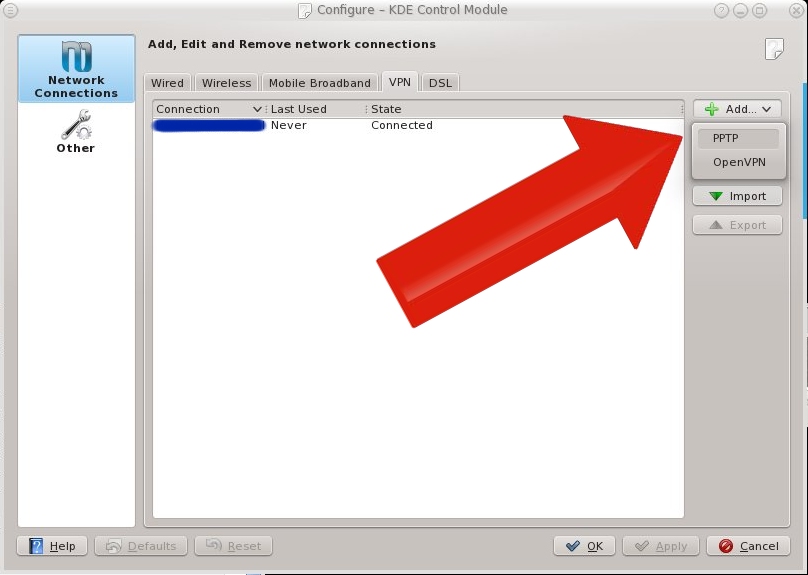
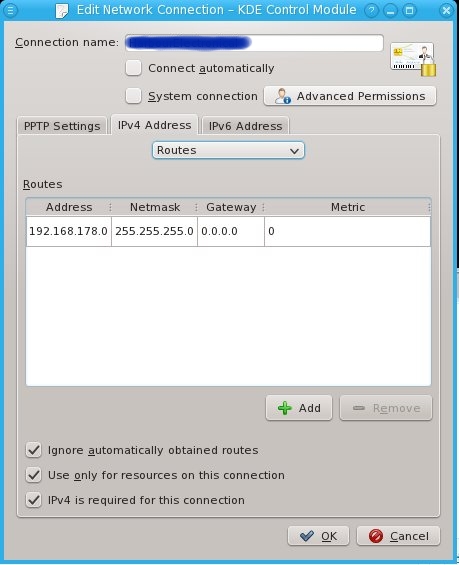
In the KDE Network Manager plasma module, go to the tab VPN, click add and choose PPTP.
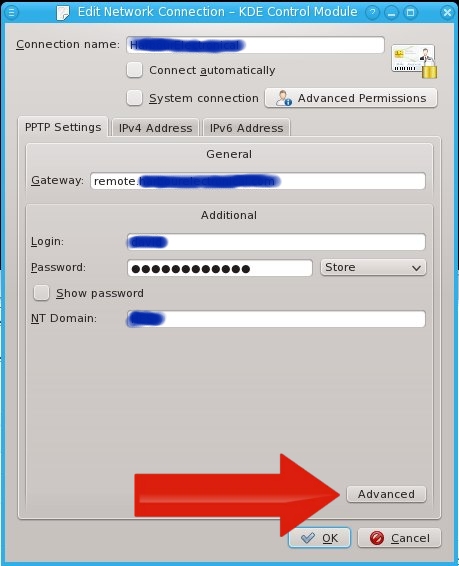
Enter and connection name you like. In the field "gateway" type the hostname or IP number of the Windows server you're connecting to. Under Login, Password and NT Domain, fill in your authentication data. Then click advanced.
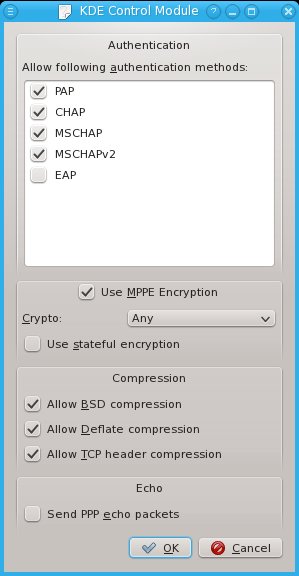
In the advanced window, disable EAP and enable MPPE. Then click OK.
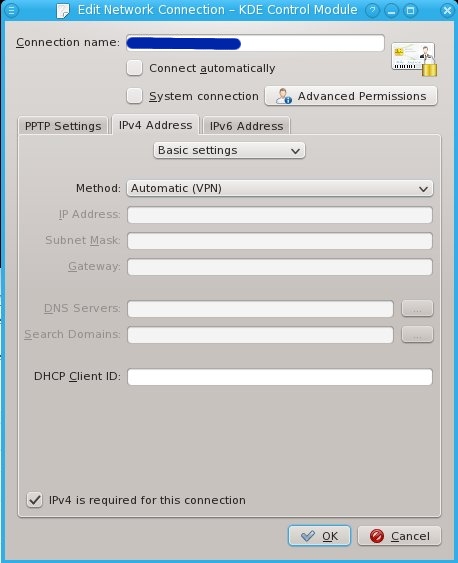
Go to the tab IPv4. Under method, I chose Automatic (VPN). But Automatic (VPN) addresses only is also a nice option: it sets the IPs but no DNS settings.
Go to the routes sub-tab. Switch on Ignore automatically obtained routes and Use only for resources on this connection to make sure the connection doesn't steal your traffic. Then I entered a manual route: 192.168.178.0/255.255.255.0 to gateway 0.0.0.0 (it is a ppp device after all).
You may want to configure IPv6 as well, but I don't at this moment, so I'm not documenting this.
Step 3: Connect
Click on the icon in the tray and connect.
Ubuntu/Debian
I'm running RedHat-based software on all of my machines. Above information may be useful for Ubuntu/Debian users, but it's not tested and I'm not supporting it.
Servers: RedHat Enterprise Linux/CentOS is more suitable for servers, as there's a lot of professional level support available. I think that's important, because if I say, get a car accident, I want the servers to be managable by another professional.
Desktops/Laptops: RPM packages are pretty exchangable between RedHat-based platforms. That's a good reason to run Fedora on the desktop.
CentOS 5's and Fedora 15's base installations are pretty good prepared to use X11 over SSH. You just need to install one more package on the server you're connecting to: xorg-x11-xauth. According to yum info, the purpose of this package is: xauth is used to edit and display the authorization information used in connecting to an X server. This editting probably means synchronising X11 authority cookies between SSH peers.
Installing is done using: yum install xorg-x11-xauth
Today I made my first native IPv6 connection. I've been running Teredo/Miredo on my laptop for quite a while now, and I thought it was time to get a real IPv6 connection. I could use IPv6 autoconfiguration, but on a server you need a fixed IP.
Needed software
Install required packages that are not included in the Fedora default install: yum install iproute2 ndisc6
Configuring manually
Configuring the network is not that much different from configuring an IPv4 address.
IPv4
IPv6
ip addr add 1.2.3.4/24 dev eth0
ip addr add 2001:1BE8:DEAD:BEEF::1a1a/64 dev eth0
ip route add default via 1.2.3.254
ip route add default via 2001:1BE8:DEAD:BEEF::1
Now test it by pinging/tracerouting some known IPv6 services: [root@localhost ~]# ping6 ipv6.google.com PING ipv6.google.com(2a00:1450:8003::69) 56 data bytes 64 bytes from 2a00:1450:8003::69: icmp_seq=1 ttl=58 time=7.19 ms 64 bytes from 2a00:1450:8003::69: icmp_seq=2 ttl=58 time=7.52 ms 64 bytes from 2a00:1450:8003::69: icmp_seq=3 ttl=58 time=6.98 ms 64 bytes from 2a00:1450:8003::69: icmp_seq=4 ttl=58 time=7.44 ms ^C --- ipv6.google.com ping statistics --- 4 packets transmitted, 4 received, 0% packet loss, time 3003ms rtt min/avg/max/mdev = 6.989/7.287/7.525/0.227 ms [root@localhost ~]# tracert6 ipv6.google.com traceroute to ipv6.google.com (2a00:1450:8003::69) from 2001:1be8:dead:beef::1a1a, 30 hops max, 60 bytes packets 1 2001:1be8:dead:beef::1 (2001:1be8:3f03:541::1) 1.024 ms 0.970 ms 1.036 ms 2 2001:1be8::310:1 (2001:1be8::310:1) 2.618 ms 2001:1be8::300:1 (2001:1be8::300:1) 2.583 ms 2001:1be8::310:1 (2001:1be8::310:1) 2.527 ms 3 pr61.ams04.net.google.com (2001:7f8:1::a501:5169:1) 2.865 ms 2.536 ms 2.184 ms 4 2001:4860::1:0:4b3 (2001:4860::1:0:4b3) 2.801 ms 3.156 ms 24.731 ms 5 2001:4860::2:0:66e (2001:4860::2:0:66e) 7.021 ms 6.830 ms 96.541 ms 6 2001:4860:0:1::31 (2001:4860:0:1::31) 7.092 ms 7.367 ms 12.089 ms 7 2a00:1450:8003::69 (2a00:1450:8003::69) 6.996 ms 7.550 ms 7.341 ms
Configure at boot time
Step 1. Enable IPv6 networking
vim /etc/sysconfig/network then add (or replace): NETWORKING_IPV6=yes
Step 2. Configure IPv6 addresses
vim /etc/sysconfig/network-scripts/ifcfg-eth0 then add the following lines: IPV6INIT=yes IPV6ADDR=2001:1BE8:DEAD:BEEF::1a1a/64 IPV6_DEFAULTGW=2001:1BE8:DEAD:BEEF::1
Step 3. Test
Run service network restart or reboot to test. Warning: if you do this remotely, you may lose the connection. I first locked myself out of my test machine, but I always got a KVM switch attached or VMWare console.
Security
Please remember that using IPv6 also means that there's a new entrance to your network. Use ip6tables to set up a firewall.
Ubuntu/Debian
I'm running RedHat-based software on all of my machines. Above information may be useful for Ubuntu/Debian users, but it's not tested and I'm not supporting it.
Servers: RedHat Enterprise Linux/CentOS is more suitable for servers, as there's a lot of professional level support available. I think that's important, because if I say, get a car accident, I want the servers to be managable by another professional.
Desktops/Laptops: RPM packages are pretty exchangable between RedHat-based platforms. That's a good reason to run Fedora on the desktop.
Software that is not reachable, can't be hacked. Easy as that. So if you have an cloud-based anti-spam/anti-virus filter, you can block your smtp server for badguys.
In my situation, I'm using a Windows 2008 SBS server with Exchange 2007.
Start wf.msc
Go to inbound rules
Find MSExchangeTransportWorker and double-click it to open the properties
On the tab "scope", select "These IP addresses" and add the following IPs: 'Local subnet', 127.0.0.0/8, 192.168.0.0/16, fe80::/16
Also add the IPs of your anti-spam servers as well
Then click OK
Don't forget to check that the changes actually work by both checking an IP that can connect and one that doesn't
We'll be using winbind, kerberos and ntlm to authenticate the user. This requires the clocks of the AD server and the proxy server to be synchronized. rpm -qa ntp || yum -y install ntp sed -i "s/^server /#server /g" /etc/ntp.conf echo "server YOURSERVERNAME" >> /etc/ntp.conf ntpdate YOURSERVERNAME #synchronize right now service ntpd start #and keep in sync chkconfig ntpd on #after reboot as well
Step 2. Install required software
yum install krb5-workstation samba-common authconfig squid
 chkconfig squid on
Step 3. Connect to active directory
Please note that MYCOMPANY.local and mycompany.local may be different domains due to the upper/lowercase. ADSERVER=sbs.MYCOMPANY.local DOMAIN=MYCOMPANY.local WORKGROUP=MYCOMPANY authconfig --enableshadow --enablemd5 --passalgo=md5 --krb5kdc=$ADSERVER \ --krb5realm=$DOMAIN --smbservers=$ADSERVER --smbworkgroup=$WORKGROUP \ --enablewinbind --enablewinbindauth --smbsecurity=ads --smbrealm=$DOMAIN \ --smbidmapuid="16777216-33554431" --smbidmapgid="16777216-33554431" --winbindseparator="+" \ --winbindtemplateshell="/bin/false" --enablewinbindusedefaultdomain --disablewinbindoffline \ --winbindjoin=Administrator --disablewins --disablecache --enablelocauthorize --updateall
I found some information saying that /var/cache/samba/winbindd_privileged should be chowned 750 to root:squid or that you should add user squid to group wbpriv. Also, squid.conf should not have cache_effective_group defined. However, this part was not relevant on my Centos 5.6. The reason could be that I installed 5.4, then upgraded, i'm not sure. Just leaving it as a note.
Now check your winbind connection using the following commands: wbinfo -u wbinfo -g
Step 4. Configure squid
auth_param ntlm program /usr/bin/ntlm_auth --helper-protocol=squid-2.5-ntlmssp
 auth_param ntlm children 5
 auth_param ntlm keep_alive on
 acl our_networks src 192.168.0.0/16
 acl ntlm proxy_auth REQUIRED
 http_access allow our_networks ntlm
 authenticate_ip_ttl 900 seconds
This will allow all valid, logged in users to surf the web. You could also limit which users can surf by adding --require-membership-of=ADGROUPNAME to the ntlm_auth command
Start Squid using /sbin/service squid restart and you're good to go.
You may want to check what else I'm writing on Squid. I'm planning to document a lot more in the next few weeks.
Say you're living in China, and you have no web freedom whatsoever. Or in the Netherlands, and your favorite linux distro download site has been blocked by the corrupt "elite". Then having a tunnel to outside the country could be very useful.